What our reports contain
Each specimen shows a report our products generate, section by section, with the cover fields, headings and table columns the report uses. The specimens are structure only: they contain no client, case or collection data.
 Gov AI
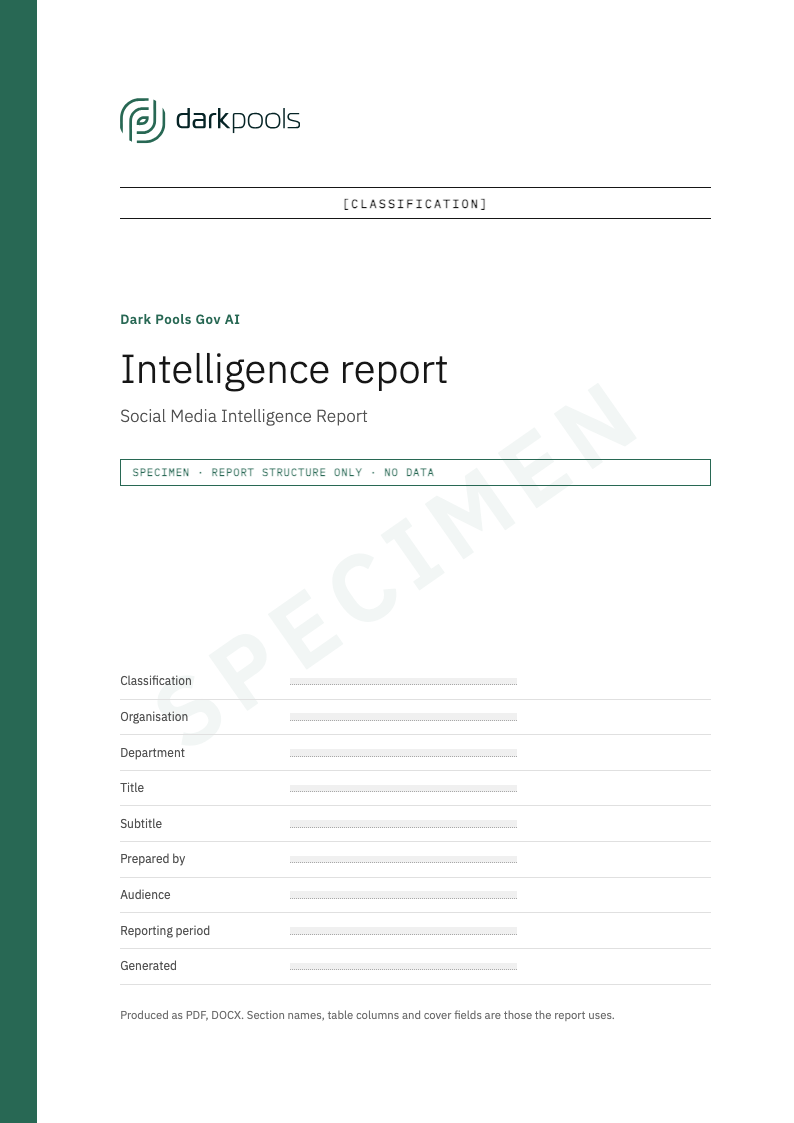
Intelligence report
The report Gov AI produces from a collection or investigation: a summary for decision-makers, the collection snapshot, the narratives, actors, claims and events found, an analytic assessment with confidence and risk, and an appendix of every source with its permalink.
Produced as PDF, DOCX
20 sections
- Executive Summary
- Collection SnapshotMetric · Value
- Sentiment DistributionSentiment · Items
- Platform BreakdownPlatform · Posts · Share
- Activity Over Time
- Situation Overview
- Sentiment & Narrative Analysis
- Platform Dynamics
- Risk Assessment
- Key ActorsAccount · Platform · Posts · Engagement
- Prominent HashtagsHashtag · Mentions
- Narratives DetectedNarrative · Severity · Assessment · Evidence
- Key Actors & NetworksActor · Role · Assessment · Evidence
- Claims & Verification StatusClaim · Analytic assessment · Evidence
- Sequence of EventsWhen · Event · Evidence
- Entities IdentifiedEntity · Type
- Key Findings
- Analytic AssessmentConfidence · Risk Level
- Recommendations
- Appendix A — Sources & Evidence# · Platform · Account · Excerpt · Permalink
 Gov AI
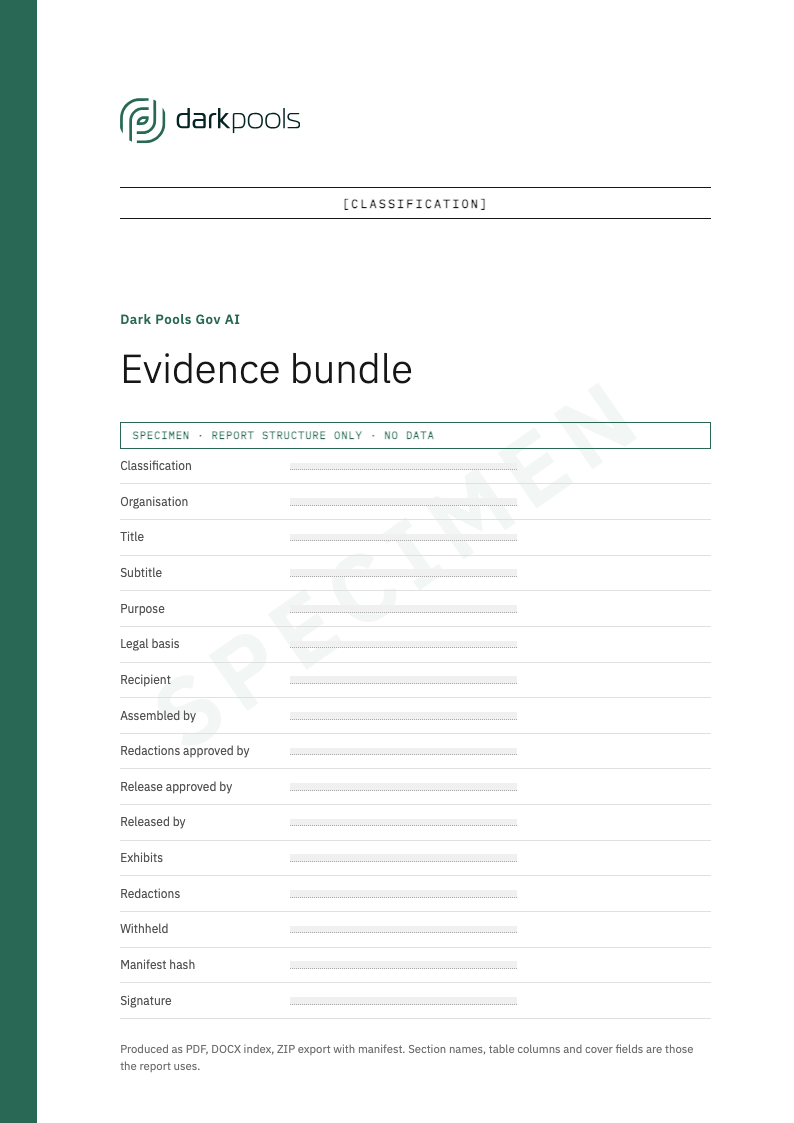
Evidence bundle
A sealed disclosure of exhibits for a case or referral: an index, one page per exhibit with its hashes, continuity checks and redactions, a disclosure schedule and an integrity statement, exported with its manifest.
Produced as PDF, DOCX index, ZIP export with manifest
9 sections
- Index of exhibitsNo. · Type · Caption · Asserts · Content hash · Redactions
- Exhibit 001 (one page per exhibit)Field · Value
- ContinuityCheck · Status
- Redactions on this exhibitItem · Disposition · Count · Reason · Classification
- Rendition (as disclosed)
- Disclosure schedule
- Reason codes usedCode · Meaning · Applies to
- Assertion vocabularyWord · Meaning
- IntegrityField · Value
 FinCrimes
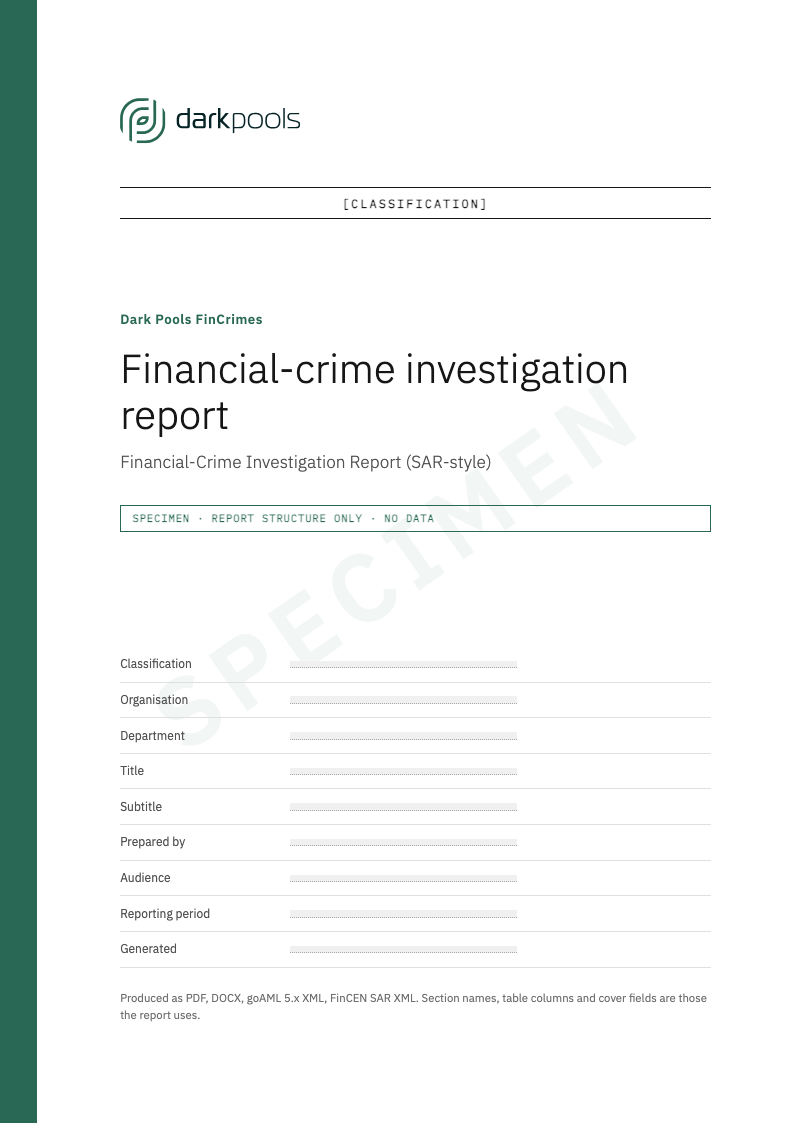
Financial-crime investigation report
The investigation report FinCrimes produces for a case, batch or workspace: the detection snapshot, severity and typology breakdowns, the suspect network, key subjects, findings, an analytic assessment, recommendations and the flagged records behind them. Cases also produce filing drafts in goAML and FinCEN SAR formats.
Produced as PDF, DOCX, goAML 5.x XML, FinCEN SAR XML
15 sections
- Executive Summary
- Detection SnapshotMetric · Value
- Severity DistributionSeverity · Alerts
- Typology BreakdownTypology · Alerts · Share
- Activity Over Time
- Detection Overview
- Typologies & Exposure
- Suspect Network & Rings
- Risk & Regulatory Assessment
- Key SubjectsSubject · Kind · Alerts · Risk score
- Key Findings
- Analytic AssessmentConfidence · Risk Level
- Recommendations
- Appendix A — Sources & Evidence
- Filing drafts (goAML 5.x and FinCEN SAR)Field · Value
 Cybersecurity
Executive security report
The board-level view of security posture from our vulnerability management work: open findings by severity, the riskiest assets, the most prevalent CVEs, how long findings stay open, the critical ones to know about and what to do next.
Produced as DOCX
8 sections
- Executive summary
- Posture at a glanceMetric · Value
- Open findings by severitySeverity · Open findings
- Top risky assetsAsset · Risk · Open findings
- Most prevalent CVEsCVE · Affected findings · Severity
- Vulnerability aging (open)Age bucket · Total · Critical + High
- Notable critical findingsFinding · Asset · CVSS
- Recommendations
 Cybersecurity
Vulnerability management programme report
The steering-committee report for a vulnerability management programme: its KPIs, risk and accountability by department, the owners with the most overdue fixes, the top risks needing attention, NIST CSF posture and the six-month remediation trend.
Produced as DOCX
7 sections
- Programme summary
- Programme KPIsKPI · Value
- Risk & accountability by departmentDepartment · Risk · Open · Overdue
- Owner scorecard (most overdue)Owner · Open · Overdue · Risk
- Top risks requiring attentionFinding · Sev · Owner · Due · Overdue
- NIST CSF postureFunction · Score · Focus
- Remediation trend (6 months)Month · Discovered · Remediated
See a report built from your own data
In a demonstration we generate these reports from your sources, in your environment, so you can judge them on material you know.